Security teams need evidence, but more data is not automatically better evidence.
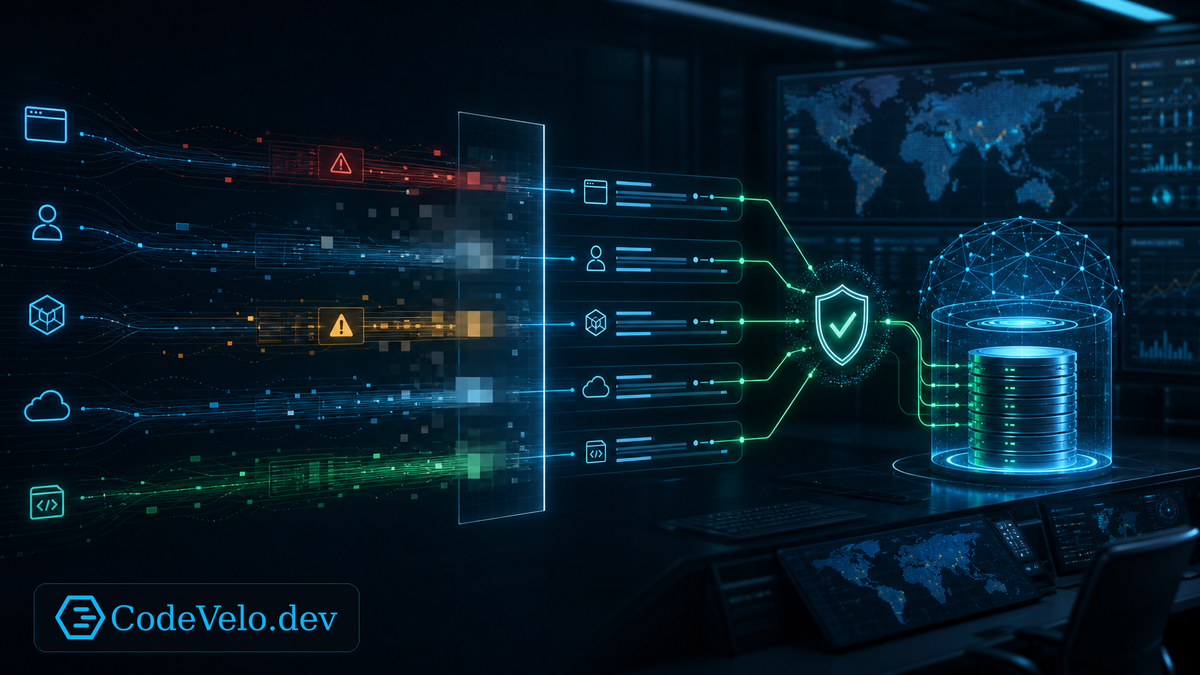
Collecting every field, payload, keystroke, and user action creates privacy risk, storage cost, investigative noise, and another valuable dataset to protect. Useful logging begins with the questions responders need to answer.
The goal is accountable systems, not continuous observation of people.
Define The Security Question
Start with decisions such as: Who authenticated? Which privileged action occurred? What permission changed? Which service accessed a protected resource? What configuration or deployment changed before the incident?
Design events for those questions. Avoid copying entire requests or records when an event type, actor identifier, resource identifier, outcome, and correlation ID are enough.
Purpose should determine collection.
Minimize Sensitive Data
Never log passwords, session tokens, API keys, private keys, or full payment data.
Classify personal and customer data before it enters telemetry. Redact or tokenize sensitive identifiers where possible. Keep debugging payload capture separate, exceptional, time-limited, and tightly authorized.
Logs are production data and need production-grade handling.
Protect Integrity And Access
Export important security events away from the system that generated them. Control who can search, export, alter, or delete logs. Record administrative access to the logging platform.
Synchronize time, define retention by purpose and obligation, and test that expected events arrive. Missing evidence should be detectable.
Make Events Actionable
Use stable schemas, clear outcomes, risk context, and correlation across identity, application, infrastructure, and deployment systems.
Tune alerts around meaningful behavior rather than every failure. Preserve enough context for investigation without forcing responders to reconstruct basic relationships manually.
Run The Defense Test
Identify who and what is trusted to produce evidence. Control access to telemetry. Separate and minimize data to limit exposure. Preserve integrity and useful retention. Maintain alternate evidence paths when one system is compromised.
Good security logging makes incidents explainable without making ordinary users excessively observable.