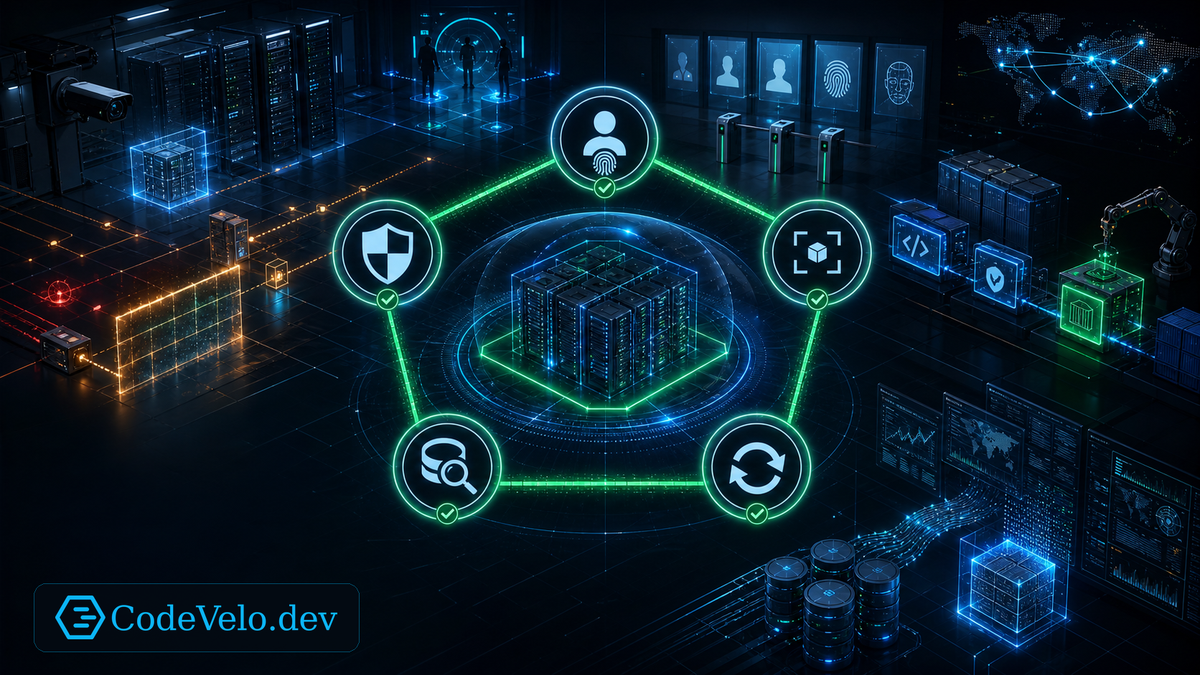
Security controls become trustworthy when they work together.
Physical access, network segmentation, authentication, authorization, secrets, supply chain policy, logging, vendor access, and recovery each protect a different boundary. The Defensible Stack Audit checks whether those boundaries reinforce one another or leave hidden paths around them.
This is the October security checklist.
1. Map Trust
List critical people, devices, services, vendors, networks, credentials, registries, recovery systems, and physical locations.
For each relationship, record why trust exists, what it permits, who owns it, and when it was last reviewed. Remove assumptions based only on network location, employment, or successful authentication.
2. Review Access Lifecycles
Check how physical badges, application roles, service accounts, secrets, vendor sessions, build permissions, management access, and emergency credentials are granted and removed.
Find shared identities, permanent exceptions, stale roles, unused tokens, expired projects, former vendors, and access without a current sponsor. Prefer named, narrow, time-bound authority.
3. Test Containment
Verify that guest devices, users, building systems, cameras, production services, management planes, backups, and administrative tools are separated according to risk.
Test blocked paths as well as allowed workflows. Review cross-tenant authorization, privileged application actions, east-west network movement, and dependency execution boundaries.
4. Validate Evidence
Confirm that physical entry, authentication, authorization changes, privileged actions, configuration, deployment, vendor sessions, and recovery activity produce useful records.
Protect log integrity, synchronize time, minimize sensitive data, define retention, and test whether missing events are detected.
5. Exercise Recovery
Test out-of-band access, emergency credentials, secret rotation, configuration restoration, rollback, backup recovery, vendor escalation, and incident decision authority.
Confirm that recovery controls remain available when production identity, networking, or infrastructure cannot be trusted. Revoke temporary access after every exercise.
Keep The Stack Defensible
Turn findings into owned work with deadlines, evidence of completion, and retesting. Revisit controls after architectural changes, incidents, vendor transitions, and major releases.
Ask the Defense Test at every layer:
- What is being trusted?
- How is access granted and removed?
- What limits the blast radius?
- What evidence survives an incident?
- How does the system recover safely?
Security improves when those answers are intentional and connected.