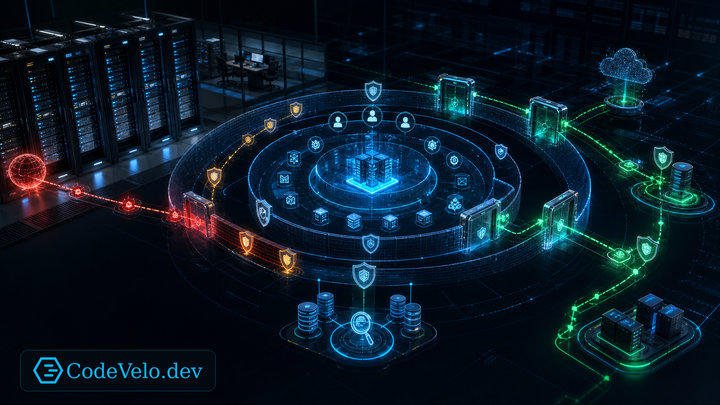
The Defensible Stack: CodeVelo's Defense-in-Depth Framework
A defensible stack limits trust, contains failure, preserves evidence, and provides safe recovery from the rack to the runtime.
Topic
A defensible stack limits trust, contains failure, preserves evidence, and provides safe recovery from the rack to the runtime.
Documentation stays trustworthy when it is owned, tested against reality, and updated through the same workflow as the system.
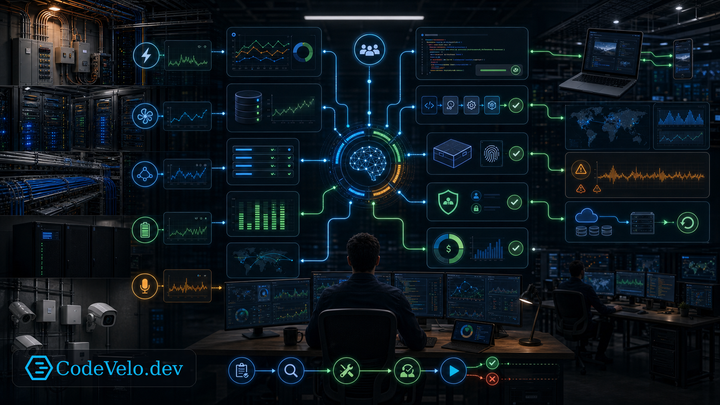
A measured stack connects physical telemetry, application events, cost, capacity, privacy, and recovery into one operational intelligence loop.
Automation should be fast, observable, bounded, and reversible. This July checklist reviews trust from the wiring closet to the deployment pipeline.
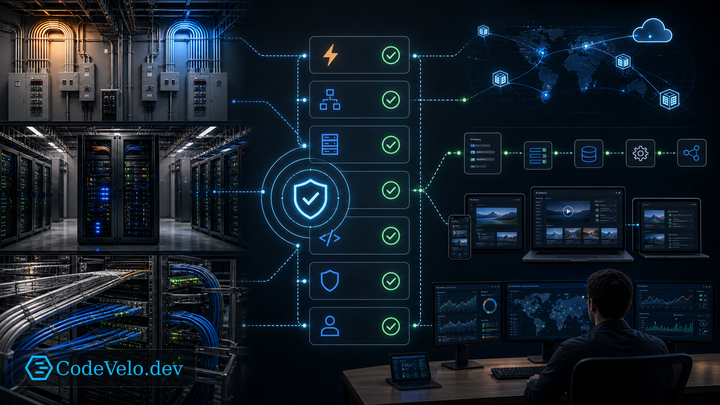
A practical hardening checklist that connects the physical layer, the network, the application, and the browser into one resilience review.
The CodeVelo Audit connects infrastructure, software delivery, and business operations. It helps teams find the bottlenecks that sit between network hardware and application code.
Fiber-to-the-desk starts to matter when distance, bandwidth, EMI, or heat make copper the wrong fit. The decision should follow workload and facility constraints.