Security is not a product added at the edge of a finished system.
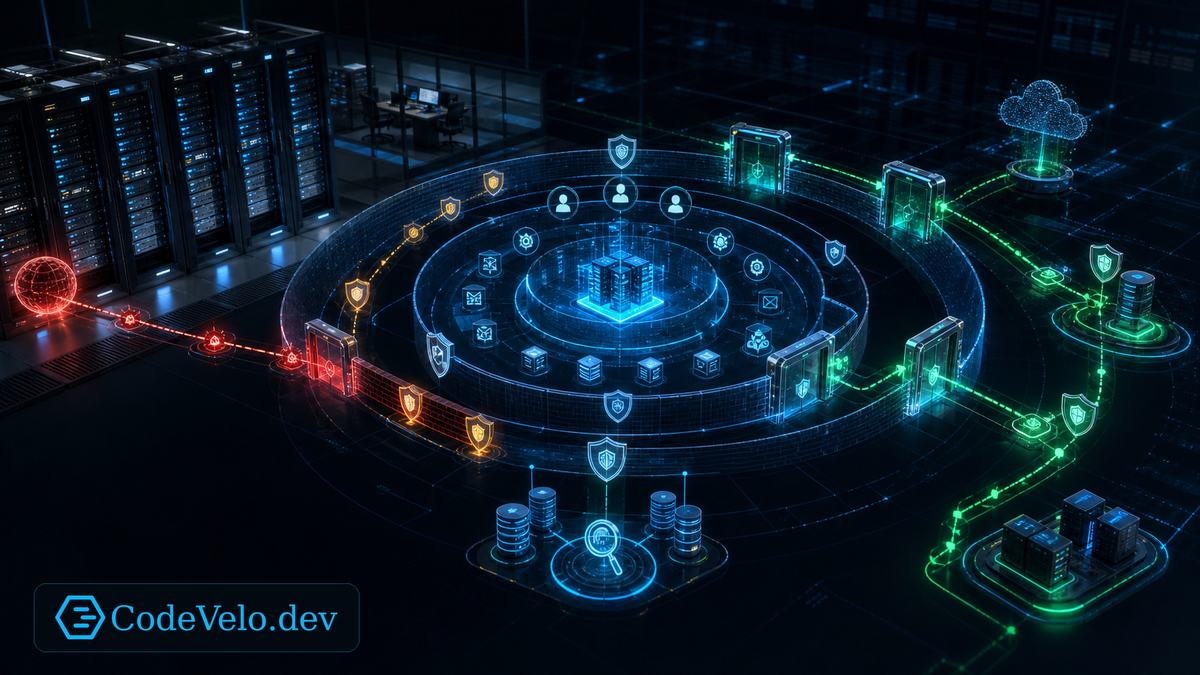
It is the way trust, access, evidence, isolation, and recovery are designed across the physical room, the network, the application, and the operating process. A single strong control cannot compensate for every weak layer around it.
A defensible stack assumes that controls can fail and makes sure one failure does not become total compromise.
Make Trust Explicit
Every trusted path should have a reason.
Document which people, devices, services, vendors, credentials, and networks can reach a resource. Separate identity from authority. A valid login should not imply broad access, and a managed device should not automatically become trusted everywhere.
Trust should be narrow, reviewable, and temporary where possible.
Limit The Blast Radius
Segmentation matters at every layer.
Separate physical management, user traffic, cameras, building systems, production services, administrative interfaces, data stores, and deployment controls according to risk. Inside applications, isolate tenants, privileges, secrets, and expensive capabilities.
Containment gives responders time to understand an incident before it spreads.
Preserve Useful Evidence
A defensible system can explain what happened.
Record authentication, authorization changes, privileged actions, configuration changes, deployments, device access, and security-control state. Protect logs from easy alteration, synchronize time, define retention, and avoid collecting unrelated personal data.
Evidence should support decisions without becoming surveillance.
Design Recovery With Security
Recovery paths are part of the security boundary.
Backups, out-of-band management, emergency credentials, rollback tools, and vendor access need stronger protection because they become most valuable during failure. Test them before an incident and revoke temporary authority afterward.
Run The Defense Test
For every critical system, ask:
- What is being trusted?
- How is access granted and removed?
- What limits the blast radius?
- What evidence survives an incident?
- How does the system recover safely?
A defensible stack does not promise that nothing will go wrong. It makes failure harder to cause, easier to contain, and safer to recover from.