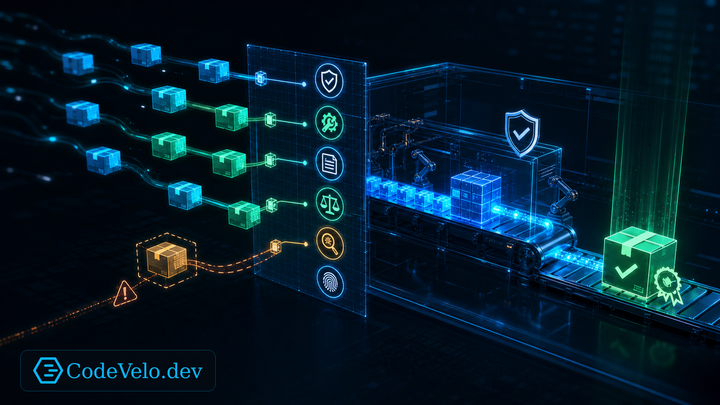
Dependency Admission Policies for the Build Pipeline
Dependency admission policies evaluate source, maintenance, license, integrity, and risk before packages enter the trusted build path.
Topic
Dependency admission policies evaluate source, maintenance, license, integrity, and risk before packages enter the trusted build path.
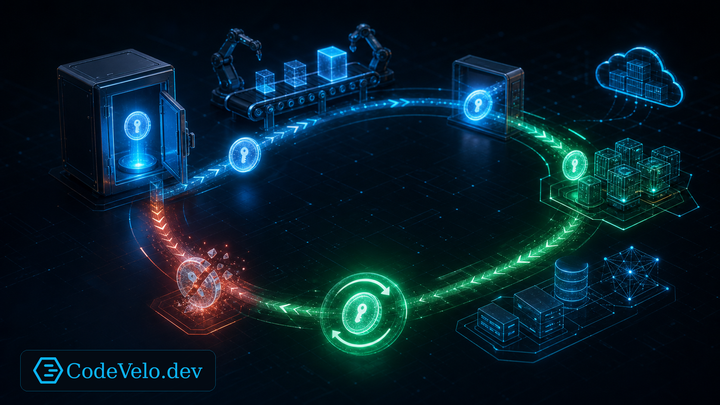
Secrets should be requested, issued, scoped, delivered, observed, rotated, revoked, and destroyed through a controlled lifecycle.
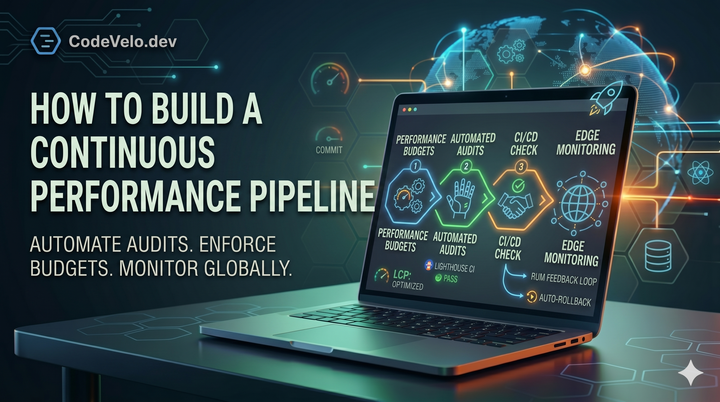
A continuous performance pipeline turns speed into a release gate. Automated audits, budgets, and monitoring keep regressions visible before they reach users.
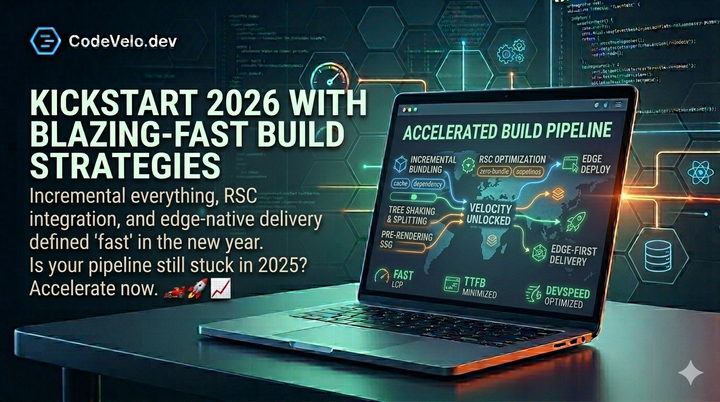
Fast build pipelines depend on incremental work, clear dependency boundaries, and practical caching. Build strategy is now part of developer experience and release reliability.