A secret is not secure merely because it is encrypted at rest.
API keys, database passwords, signing keys, certificates, and service credentials move through systems and people. They are created, delivered, cached, copied, logged, rotated, and sometimes forgotten. Each stage changes the risk.
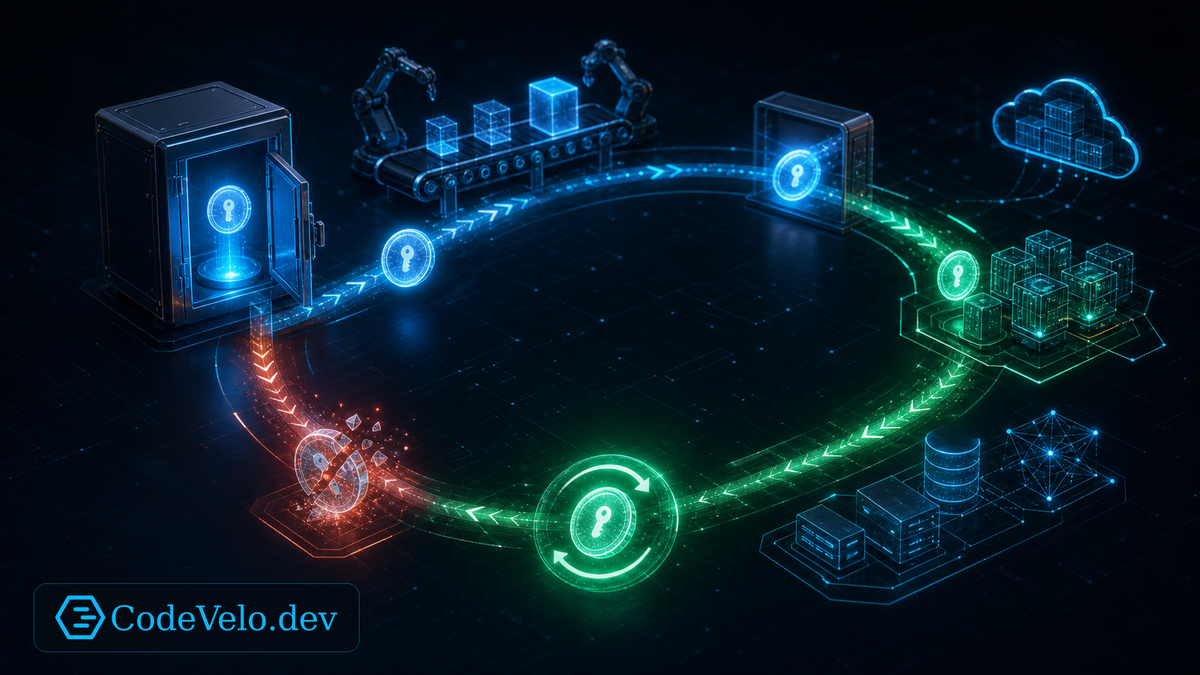
Secret management needs a complete lifecycle.
Issue Secrets For A Purpose
Every secret should have an owner, consumer, scope, environment, creation time, and expiration or review date.
Avoid credentials shared across unrelated services or environments. Prefer workload identity and short-lived credentials when the platform supports them. A production secret should not be useful from a developer laptop by default.
Narrow purpose limits blast radius.
Deliver Without Exposing
Do not place secrets in source control, container images, build logs, tickets, chat, or frontend bundles.
Use a controlled secret store and inject values only where needed. Protect access to the store with strong identity and authorization. Make sure debugging tools, crash reports, and telemetry redact sensitive values.
Encryption cannot protect a secret after it is printed into a public log.
Rotate Before An Emergency
Rotation should be a routine capability.
Support overlapping credentials when a zero-downtime transition requires it, then remove the old value promptly. Test applications that cache credentials. Track certificates and keys that need coordinated replacement.
If rotation is never rehearsed, compromise becomes the first full test.
Revoke And Verify
Remove secrets when a service, employee, vendor, integration, or environment no longer needs them. Confirm that the old credential fails and that no hidden consumer still depends on it.
Preserve evidence of issuance, access, rotation, and revocation without recording the secret itself.
Run The Defense Test
Identify what trusts the credential. Define how access begins and ends. Scope the secret to contain misuse. Preserve lifecycle evidence. Maintain a tested recovery path for emergency rotation.
A secret that cannot be rotated or revoked is not fully controlled.