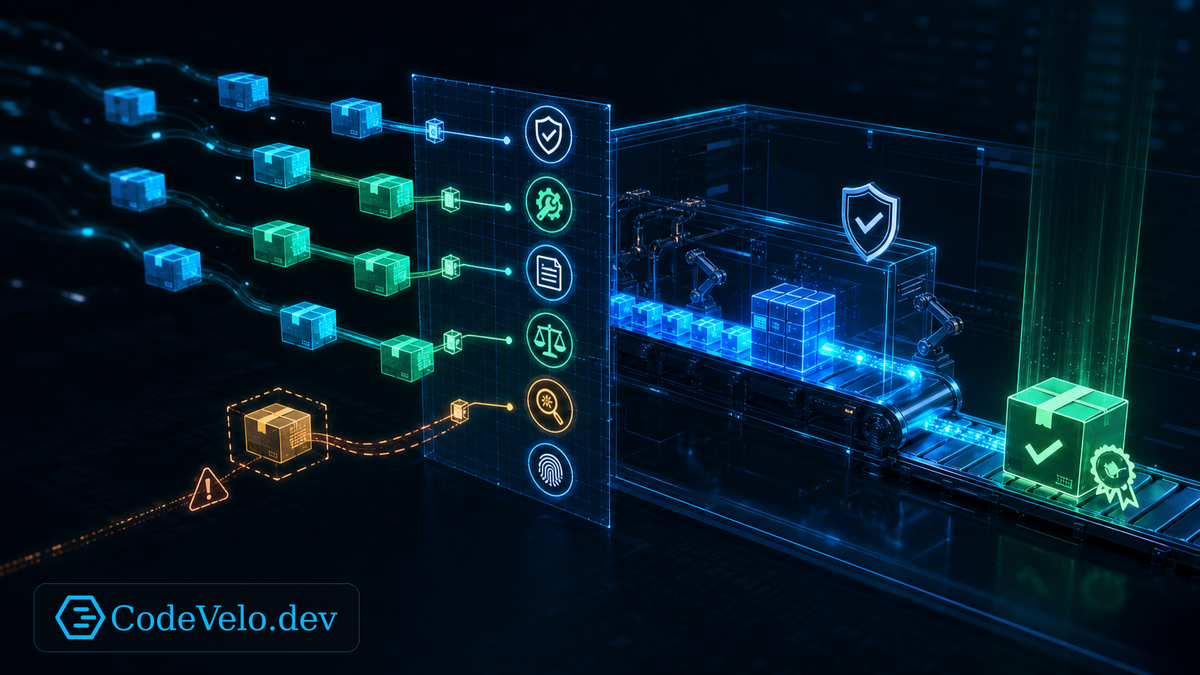
Most dependency controls begin after a package is already inside the application.
A scanner reports a vulnerability, an update bot proposes a version, and the team reacts. Those controls matter, but the first important decision happened earlier: should this dependency have entered the trusted build path at all?
Admission policy makes that decision explicit.
Evaluate The Source
Confirm the package name, registry, publisher, repository, signature or integrity data, and expected ownership.
Protect against typosquatting and unexpected registry sources. Lock versions and verify checksums. Restrict who can change registry configuration, lockfiles, and dependency policy.
Convenient installation should not silently establish permanent trust.
Review Maintenance And Necessity
Ask whether the package is actively maintained, widely understood, compatible with the platform roadmap, and necessary for the product.
Review release history, unresolved security issues, maintainer changes, transitive dependency count, native build behavior, and install scripts. Small functionality may not justify a large execution surface.
Removal is easier before adoption spreads across the codebase.
Apply Risk-Based Gates
Not every dependency needs the same approval.
Packages used in authentication, cryptography, build tooling, deployment, parsing, or privileged runtime paths deserve stronger review. Define allowed licenses, vulnerability thresholds, provenance requirements, and exception authority.
Exceptions need owners and expiration dates.
Preserve The Decision
Record why important dependencies were accepted, which version entered, what evidence was reviewed, and which controls apply afterward.
Generate a software bill of materials and connect deployed artifacts to their dependency set. When risk changes, the team should know where the package is running.
Run The Defense Test
Identify which publishers and registries are trusted. Control who may introduce or update packages. Limit dependency execution and application reach. Preserve admission and build evidence. Maintain a replacement and rollback path.
The safest vulnerability response begins before installation.